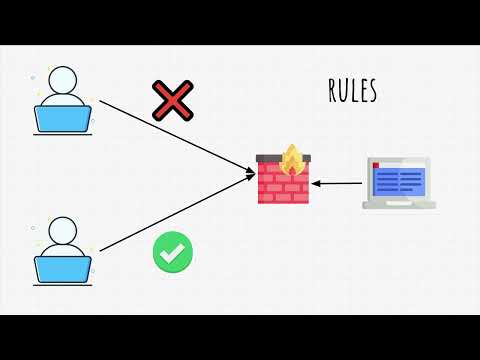
You know, there was this one time when I thought my computer had a mind of its own. Things were just popping up left and right, and it was like a digital ghost party. Not fun at all! That’s when I found out about the magic of firewalls—specifically, the host-based kind. It’s like having a friendly bouncer for your computer that helps keep out all the troublemakers.
So basically, a host-based firewall is something you install directly on your device. It keeps an eye on everything going in and out, making sure only the good stuff gets through. Kind of like how your mom approves who can come into your room for playdates!
And here’s the kicker—these firewalls can really beef up your security game without you even breaking a sweat. They help protect against those sneaky cyber threats that are always trying to get their foot in the door.
Anyway, stick around! There’s so much more about these unsung heroes that make them worth considering for anyone with a gadget and an internet connection.
Advantages of Network Host-Based Configuration
Hey, you curious soul! Let’s chat about why setting up your network with a host-based configuration can be like putting on an extra cozy layer of security. You know, sometimes, it’s the little things that make all the difference.
What’s this host-based thing? Imagine each computer in your network wearing its personal security shield. In geek terms, it’s basically when individual hosts (like computers or servers) have their own firewalls and settings instead of relying on just one big central shield for everyone. It adds a personalized touch to security!
- Stronger Security: It’s like giving each device its personal guard dog! Even if one device gets in trouble, others stay safe because they’ve got their own defenses. So you can sleep easy knowing everything’s a little bit more secure.
- Tweaked Just for You: Since each device gets its setup, you can tweak settings to suit specific needs. For instance, maybe your online shopping gateway requires tighter control than the office printer.
- Picky Permissions: Ever dealt with kids wanting different bedtime stories? Host-based configurations let you decide who accesses what and when—not every story fits all kiddos!
Picture this: Your office server handling sensitive data gets hacked—yikes! But blessedly, thanks to host-based configurations, the hacker doesn’t prance straight through to other devices in the building.
A few perks worth mentioning:
- Flexibility Galore: Each user or department might have varied usage patterns or risks (think IT vs Human Resources). With individualized setups on host devices within networks—you cater bespoke solutions seamlessly.
- Caught Red-Handed!
Here’s a funny bit: One time I was sitting at my desk scrolling through cat videos when suddenly…my screen froze (no more cute kitties!). Turned out there’d been an attempted breach—but thanks to having my nifty host-based setup—it didn’t get very far at all!
In case you’re wondering—yes—a collective sigh followed afterward! Even administrative headaches ease up too since adjustments seldom affect neighboring devices’ smooth operations following disruptions.
Neat huh?
Network-Based vs Host-Based Firewall Benefits
Hey there! Let’s get into the world of firewalls—specifically the difference between Network-Based and Host-Based Firewalls. They both play a huge role in keeping your digital life safe and sound, kind of like superheroes you can’t see but feel. So, here’s what’s up.
- Network-Based Firewalls: Imagine these as big guards at the entrance to your digital kingdom. They protect entire networks from unwanted intruders.
- Main Duty: They control traffic between different networks, especially from outside coming in.
- Where You Find Them: Usually set up on routers or dedicated servers.
- Their Strengths: They’re great at handling lots of data because they’re built into hardware. This means they don’t slow down easily!
- An Example: If you’ve got a company network, this firewall keeps out things that shouldn’t have access to any employee’s computers.
- Host-Based Firewalls: Think of these as individual shields for each device in the network. Each computer or device has its own little protector.
- Main Duty: They monitor and filter incoming and outgoing data on a single device.
- Their Place: Installed directly onto devices like computers or phones.
- Their Strengths:: Since they focus on one device, they catch threats specific to it—like if you’re downloading something fishy.
- Sensitivity: Can detect local attacks, unauthorized logins, and policy violations directly wherever it’s installed.
- Data Integrity: Keeps an eye on files and applications so any tampering or unusual activity is caught right there.
- Broad Coverage: They see everything passing through your network gates without needing access to every single device.
- No Software Hassle: Doesn’t need anything installed on individual devices since its scope is entirely external.
- Tighter Control: You’ve got more granular control when managing access per application level which adds extra security layers around unique system functions.
- User-Oriented Alerts: Since hosts filter down alert types based strictly upon what happens inside themselves—you avoid getting swamped by unnecessary noise affecting unrelated users elsewhere along cords!
, see?.. YouILikeADFF Little abilityOFFIcompany offer server!. You can also tinker with settings for specific applications depending on what you need!.
One time I had a friend who got locked out because his company’s firewall was too strict—talk about frustrating! But hey, better safe than sorry, right?, I guess? It’s all about finding balance.
Now’, putting them together usually gives you the best security blanket around. Network-based firewalls do alright when protecting large spaces like company networks~, while host-based ones add an extra layer right where it matters most–on individual devices.
So yeah’, hope that shed some light,,, peace!
Host-Based IDS vs. Network-Based IDS Advantage
You know how when you’re having a party, there’s that one friend who just stands by the door keeping an eye on who comes in and goes out? That’s kind of what an IDS does for your network. Let’s dig into Host-Based IDS (HIDS) versus Network-Based IDS (NIDS).
First off, think of a Host-Based IDS as the personal bodyguard for each computer. It’s like installing a security system inside each house on a street. It monitors activity such as file modifications or configurations specific to that particular host. One huge perk of this is sensitivity: it’s really good at spotting insider threats since it can catch unauthorized changes or behavior right there on the individual machine.
On the flip side, while HIDS are great at catching internal oddities right where they happen, they might get overwhelmed with logs from larger networks—it’s like having to read every single page of several books till you find one that’s different.
Switching gears to Network-Based IDS, imagine these as those fancy cameras that scan everyone entering a building—they monitor traffic across an entire network. NIDS analyze data sent over network wires and signals—helping you spot sketchy activities trying to sneak between systems.
Now think back to those cameras… the downside? They can’t peer into encrypted stuff or sense activity happening strictly inside each room because they’re watching from outside—so yeah, certain subtleties might go unnoticed here!
When configuring firewalls for hosts specifically linked with these systems, remember:
Both types bring different advantages depending largely upon organizational needs whether concentrated purely within isolated spots shielded fiercely via HIDS approaches or active scans covering wider territories navigated under NIDs’ watchful brows!
Ah, the good old days when I didn’t even know what a firewall was! I mean, I used to think it had something to do with fire prevention, not computers—not kidding. Host-based firewalls are like those trusty gatekeepers standing at the entrance of your computer fortress. They’re the ones ensuring that only welcome guests can come and go.
When you set one up on your computer, you basically have this extra layer of security that’s pretty invaluable in today’s digital jungle. There’s always someone out there trying to sneak their way onto your system and a host-based firewall is just one more way to shut them down. It’s like having a bouncer who’s got your back.
Now, don’t get me wrong; configuring these can be tricky sometimes. It’s kind of like figuring out a new TV remote without any instructions—where is that mute button anyway? You might find yourself tinkering around with settings that seem unfamiliar at first glance. But once you understand the basics—say, how to allow or block certain programs from accessing the internet—you’ll start feeling more in control.
But why bother setting it up in the first place? Well, having it configured properly can significantly reduce unwanted network traffic. This means fewer chances for malicious hackers poking around where they shouldn’t be poking. And who doesn’t want peace of mind knowing their personal information isn’t just being thrown around unsafely?
Think about anyone who’s ever clicked on a bad link by accident (we’ve all been there). With an extra layer of defense like this, there’s less chance for that oops moment turning into something worse.
In many ways adopting such measures feels proactive rather than reactive—and that’s a great stance when facing cybersecurity concerns! So if you haven’t fiddled with host-based firewall configuration yet perhaps give it some consideration—you’ll probably thank yourself later!